Security
What Are SIM Swap Attacks and How to Prevent Them
How to stop SIM swap attacks: enable SIM-change and port-out locks, use passkeys or security keys, avoid SMS recovery, and act fast after a swap.
•8 min read
Insights, guides, and updates from the JoltSMS team
Security
How to stop SIM swap attacks: enable SIM-change and port-out locks, use passkeys or security keys, avoid SMS recovery, and act fast after a swap.
Account Management
Check number format, carrier filters, and Uber's 'Call me' option; contact carrier or Uber and change numbers only as a last resort.
Account Management
Fix Walmart SMS verification: use a real U.S. mobile (not VoIP/landline), avoid rapid resends, and use Verify Later or Seller Support.
Communication
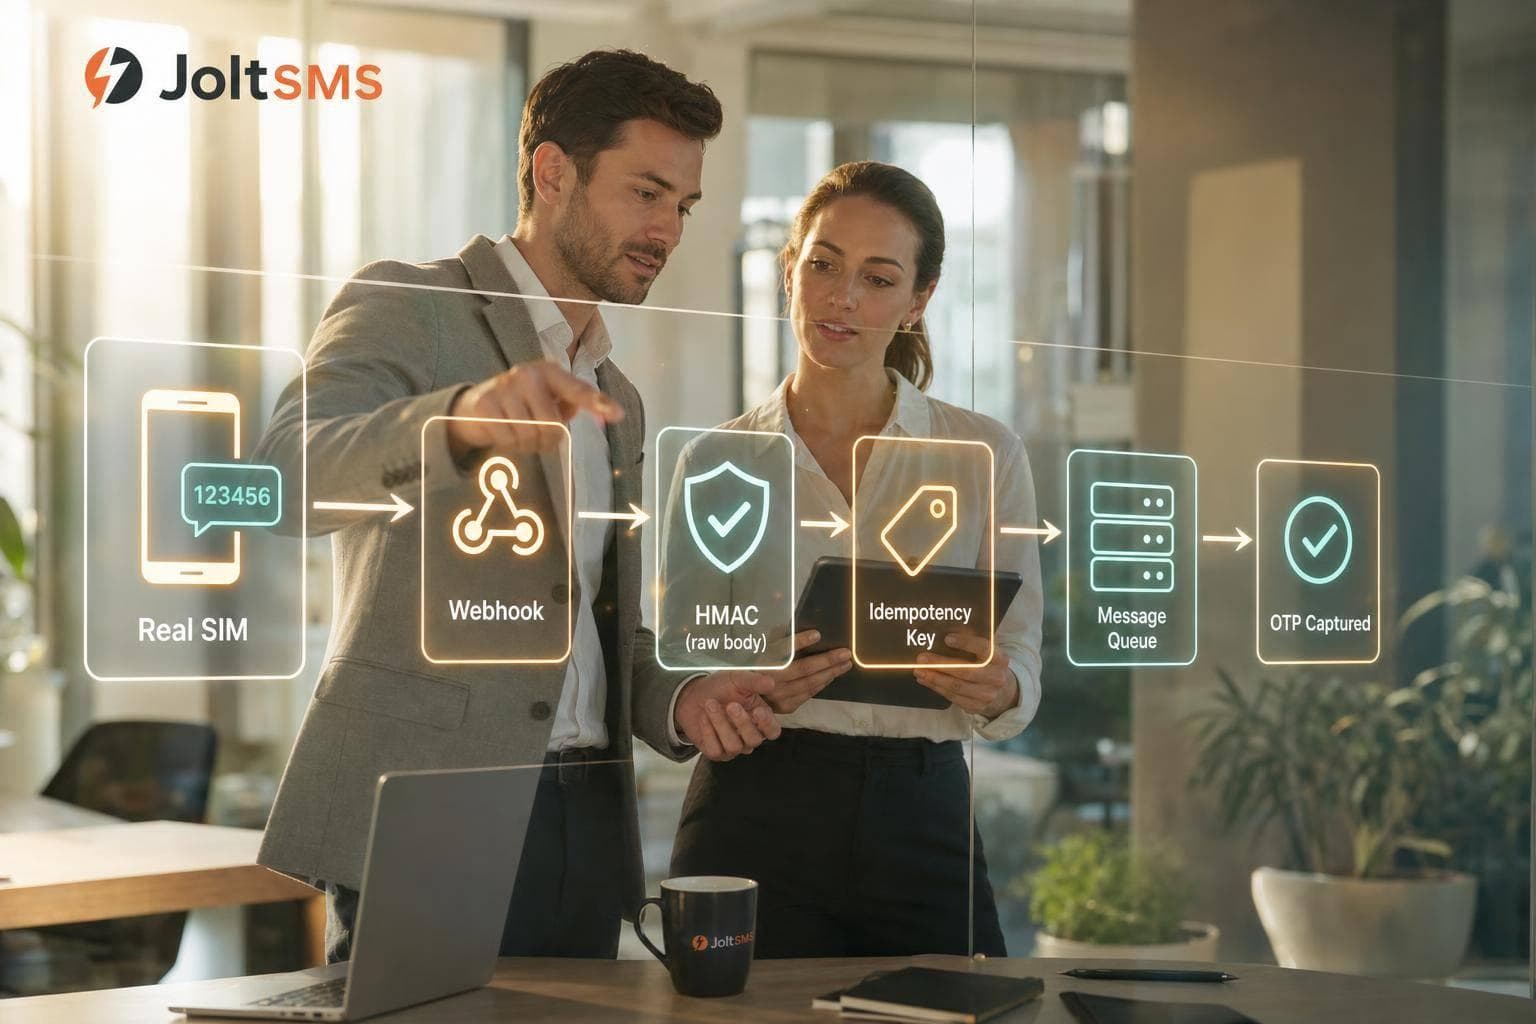
Webhooks replace polling: use real-SIM numbers, raw-body HMAC verification, idempotency, and queues to scale SMS OTP retrieval.
Communication
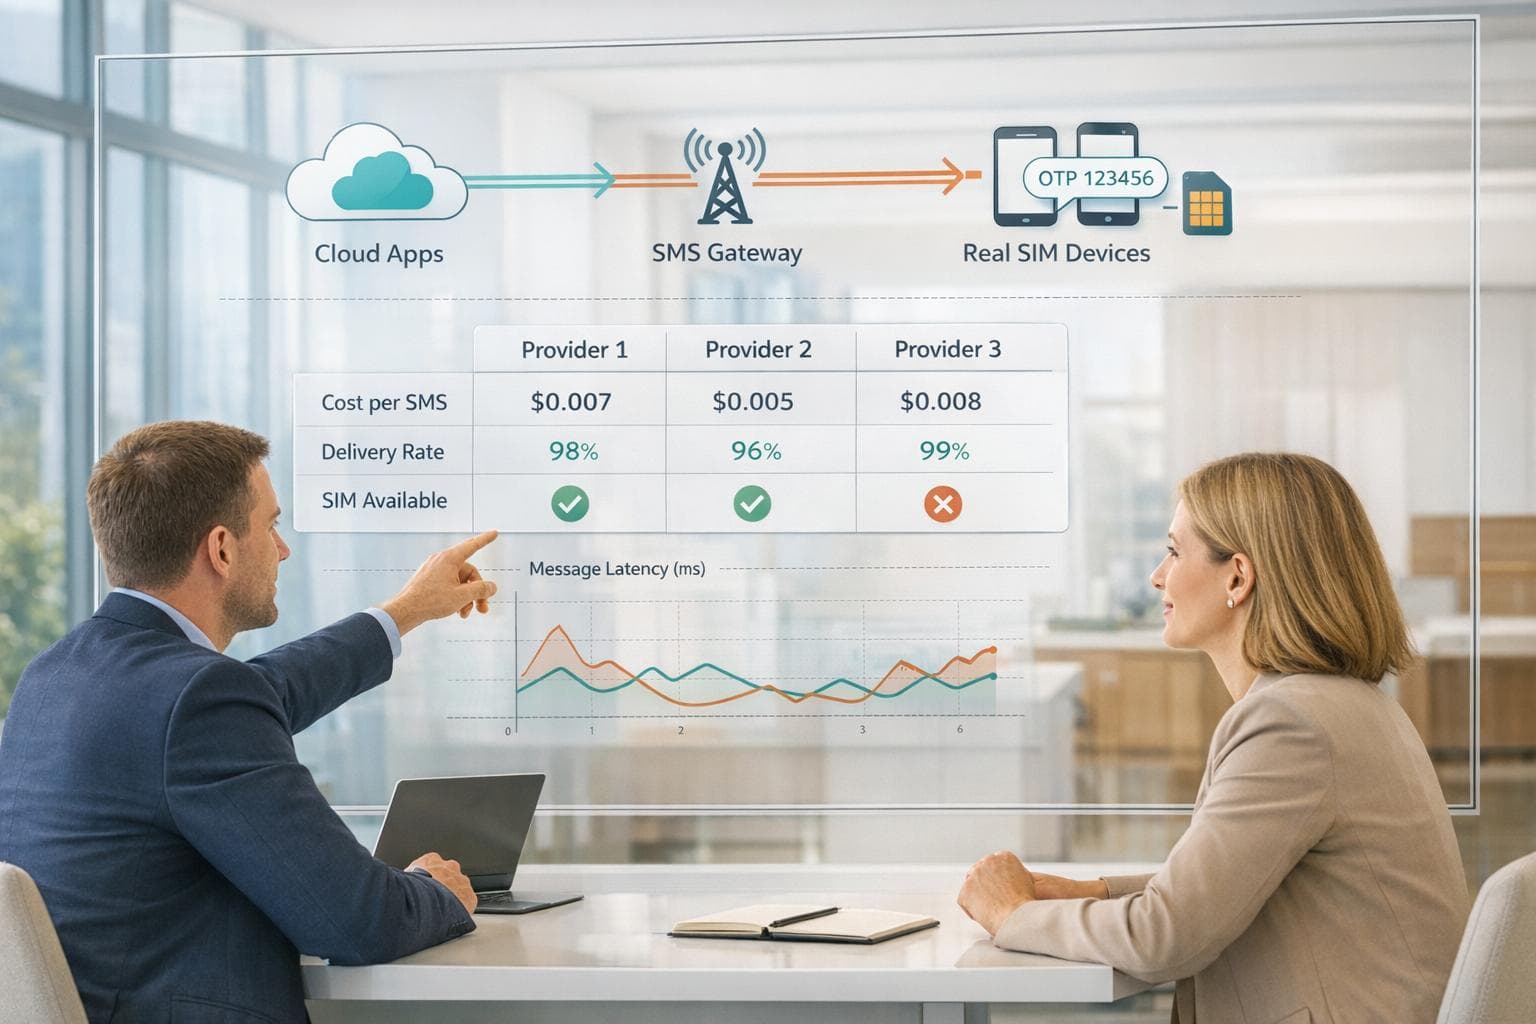
Compare SMS verification providers to find low-cost outbound APIs or real‑SIM inbound numbers for reliably receiving OTPs from banks and cloud services.
Security
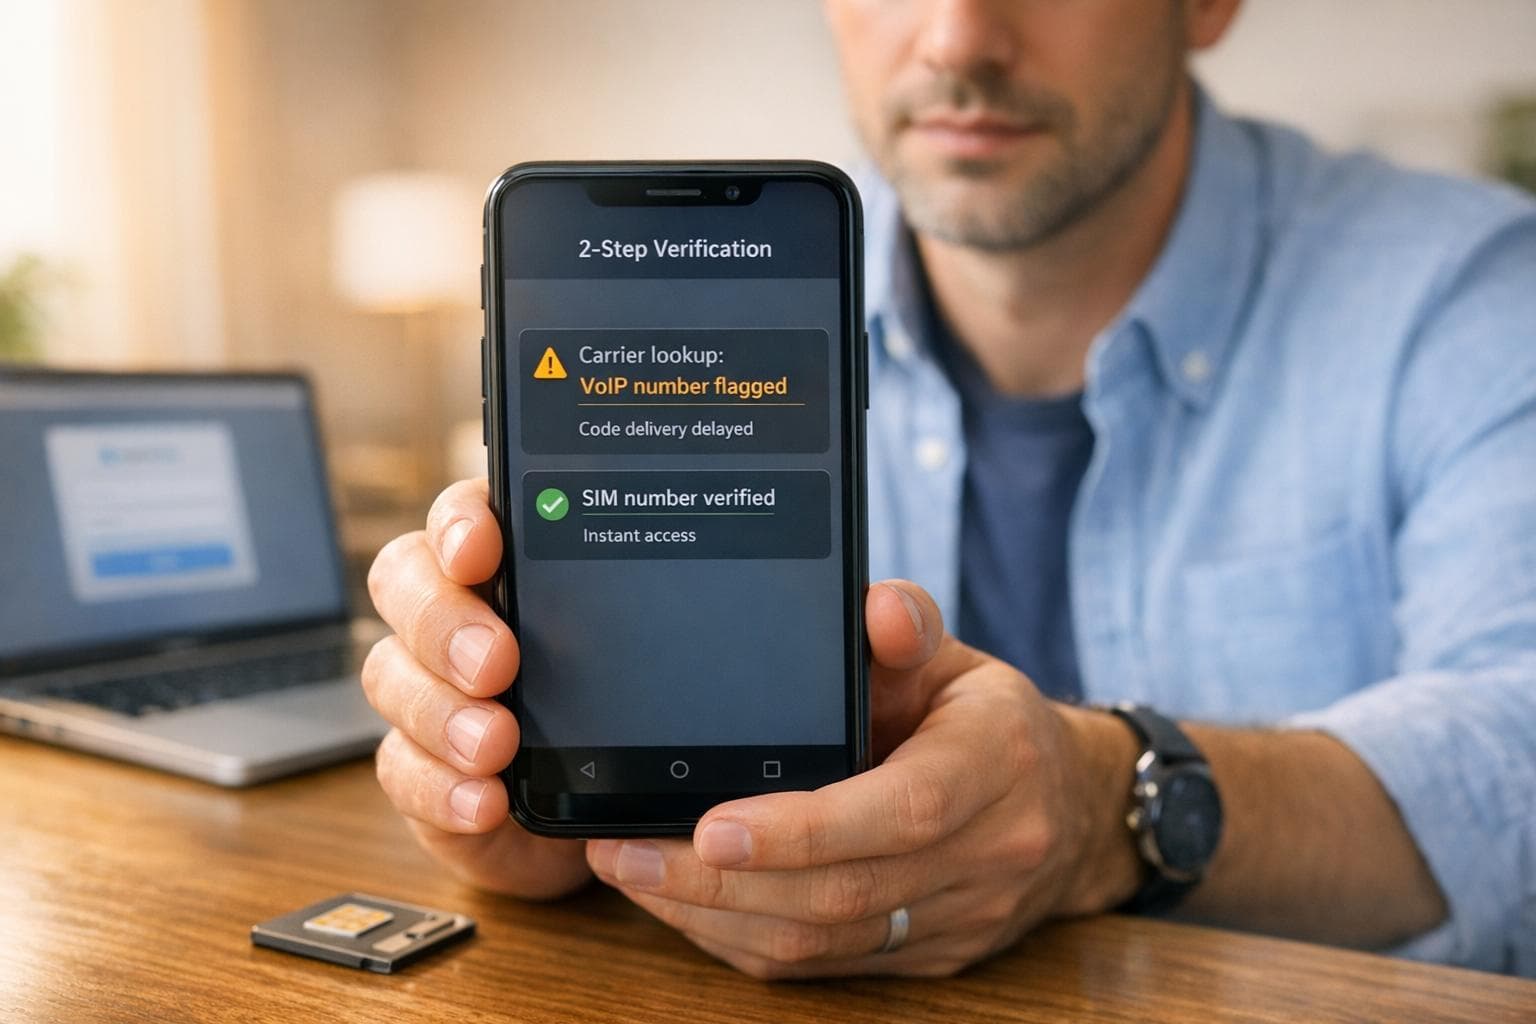
Carrier lookups flag VoIP numbers, causing delayed or failed OAuth SMS verifications. Use real SIM numbers for reliable 2FA and account access.
Security
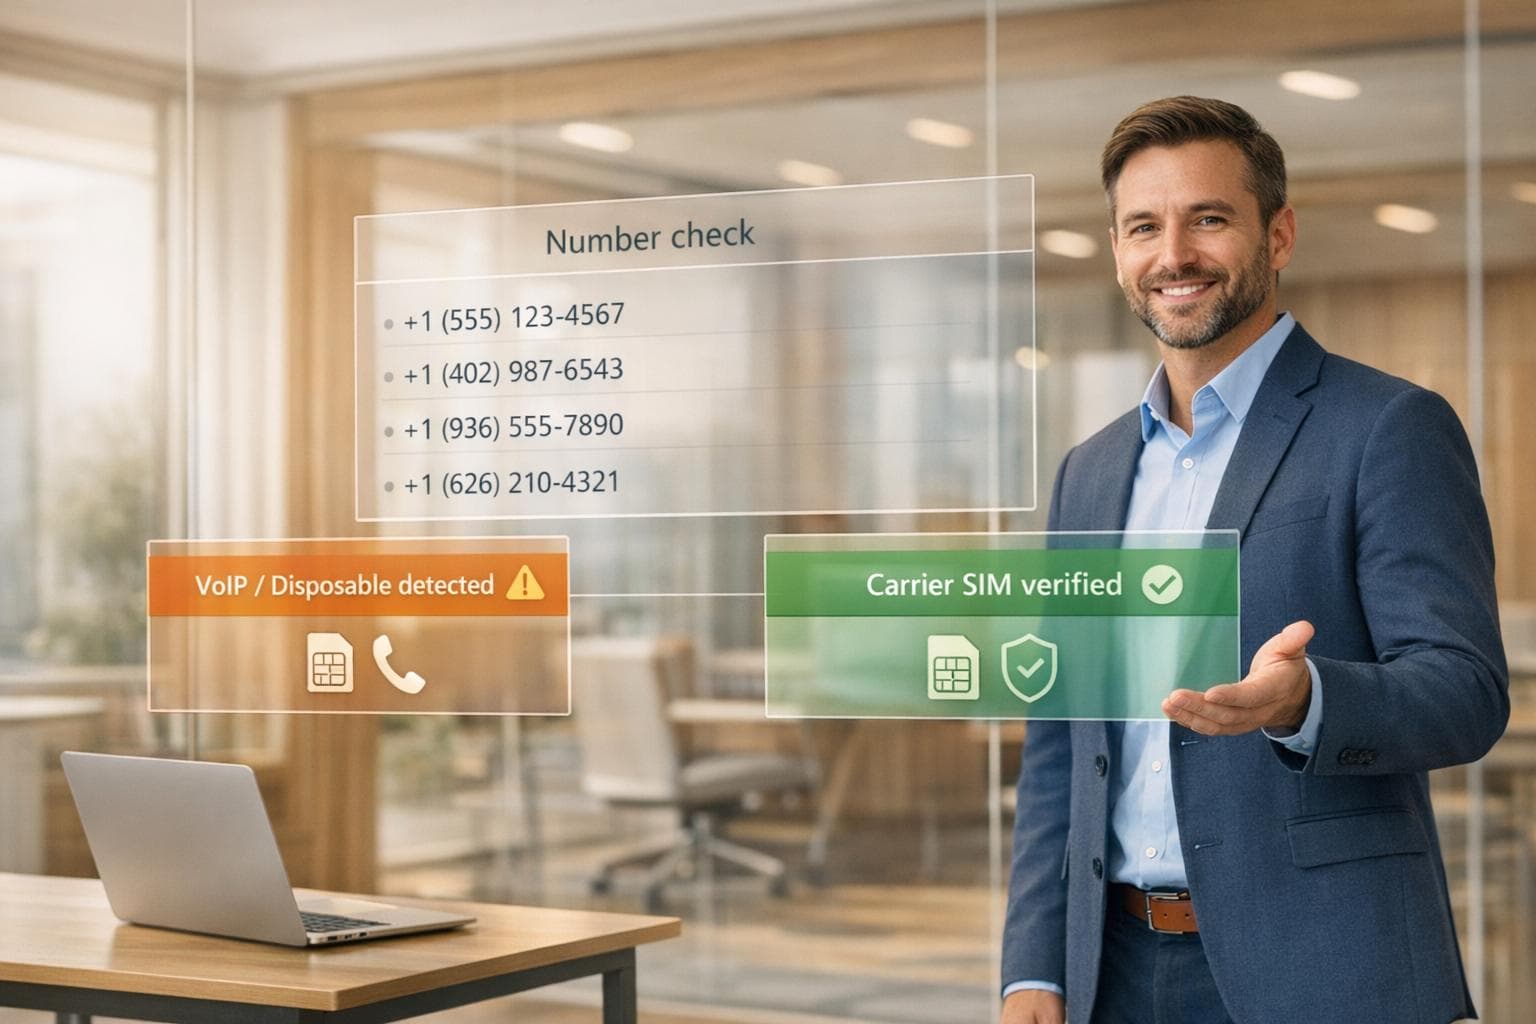
Platforms block VoIP and disposable numbers to stop fraud; learn how detection works and why carrier-issued real-SIM numbers reduce verification failures.
Account Management
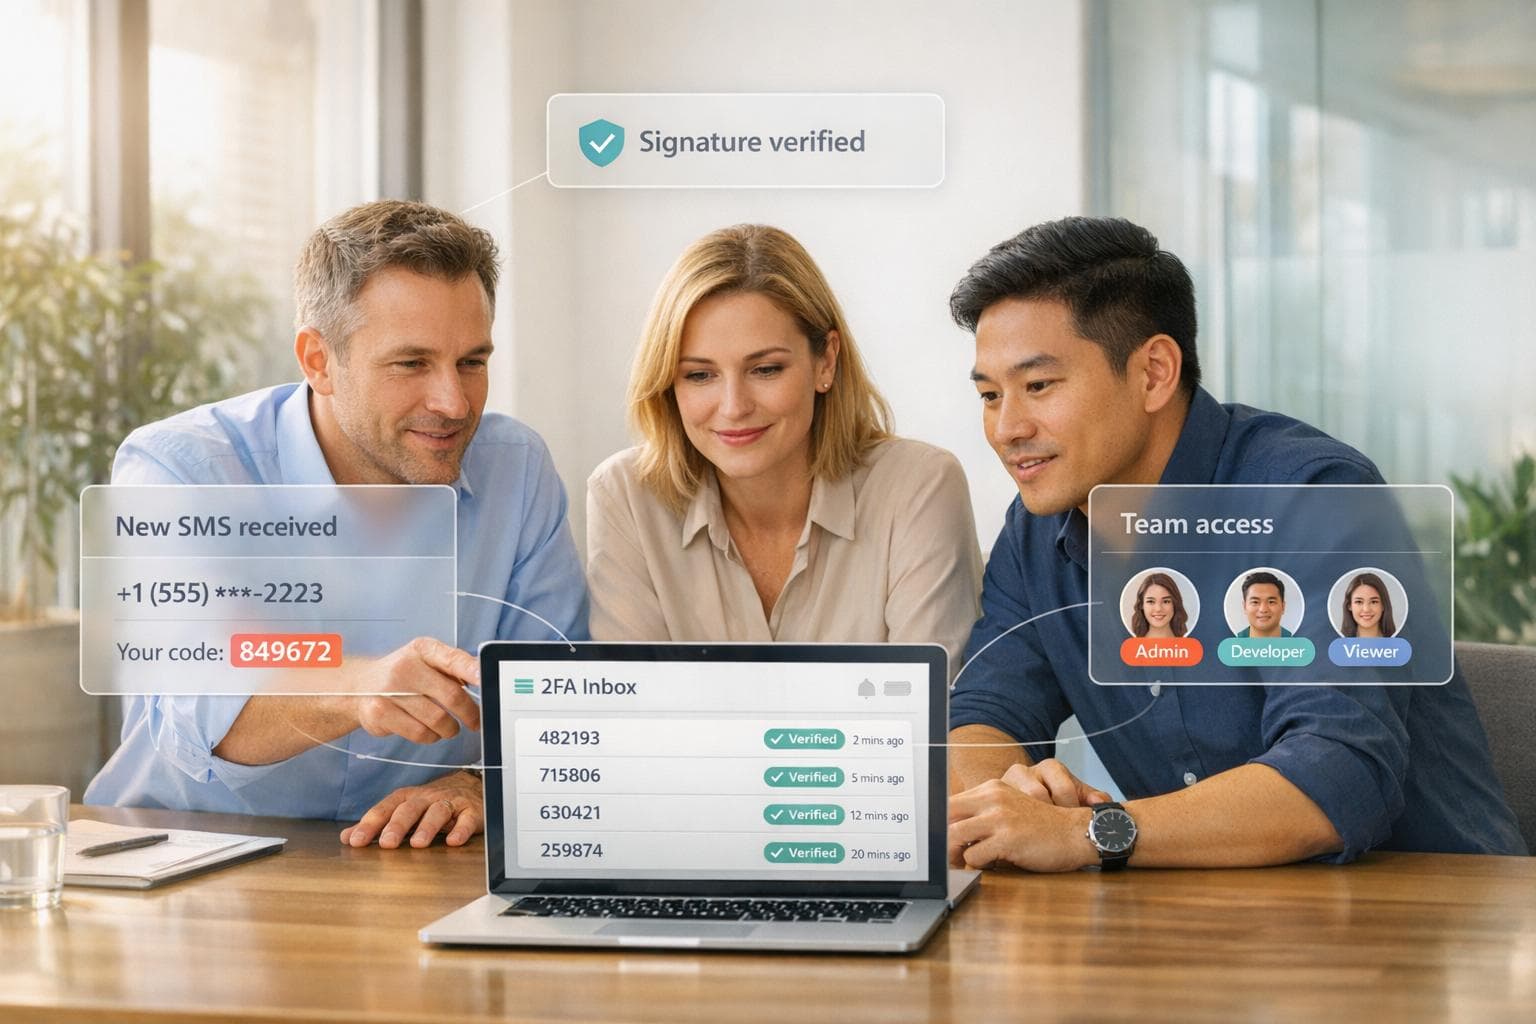
Centralize SMS 2FA codes with webhooks and APIs: receive real‑SIM OTPs, validate HMAC‑SHA256 signatures, parse and store codes, and manage team access with RBAC.
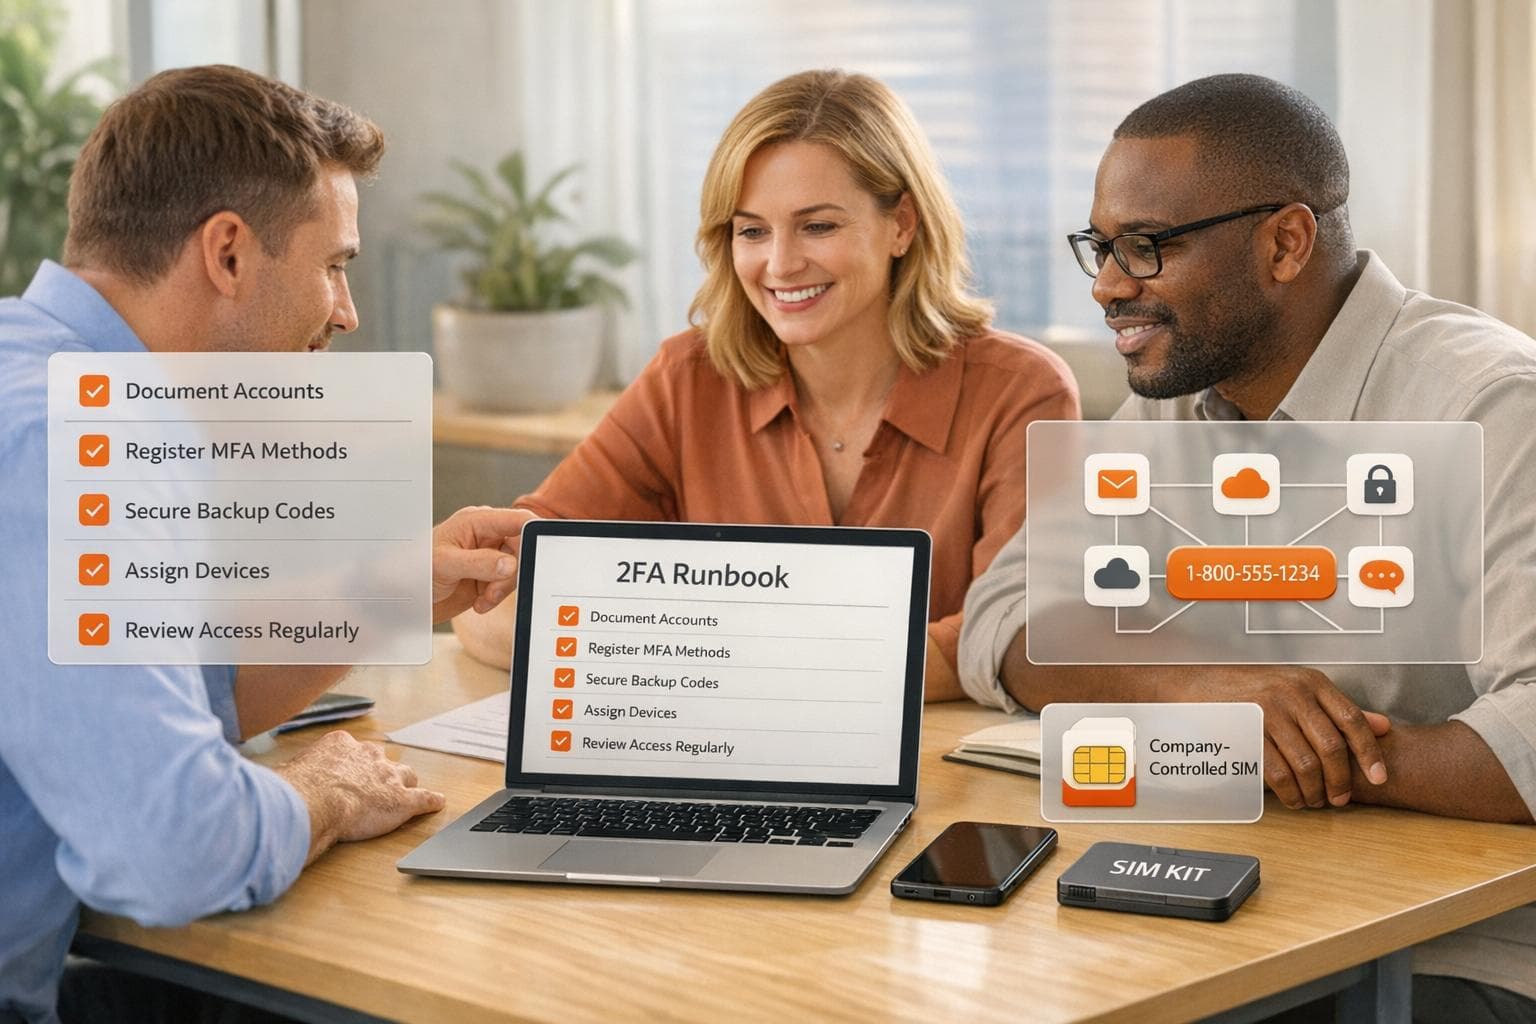
Account Management
Document every account and use company-controlled real-SIM numbers so teams can reliably access and recover 2FA-protected services.
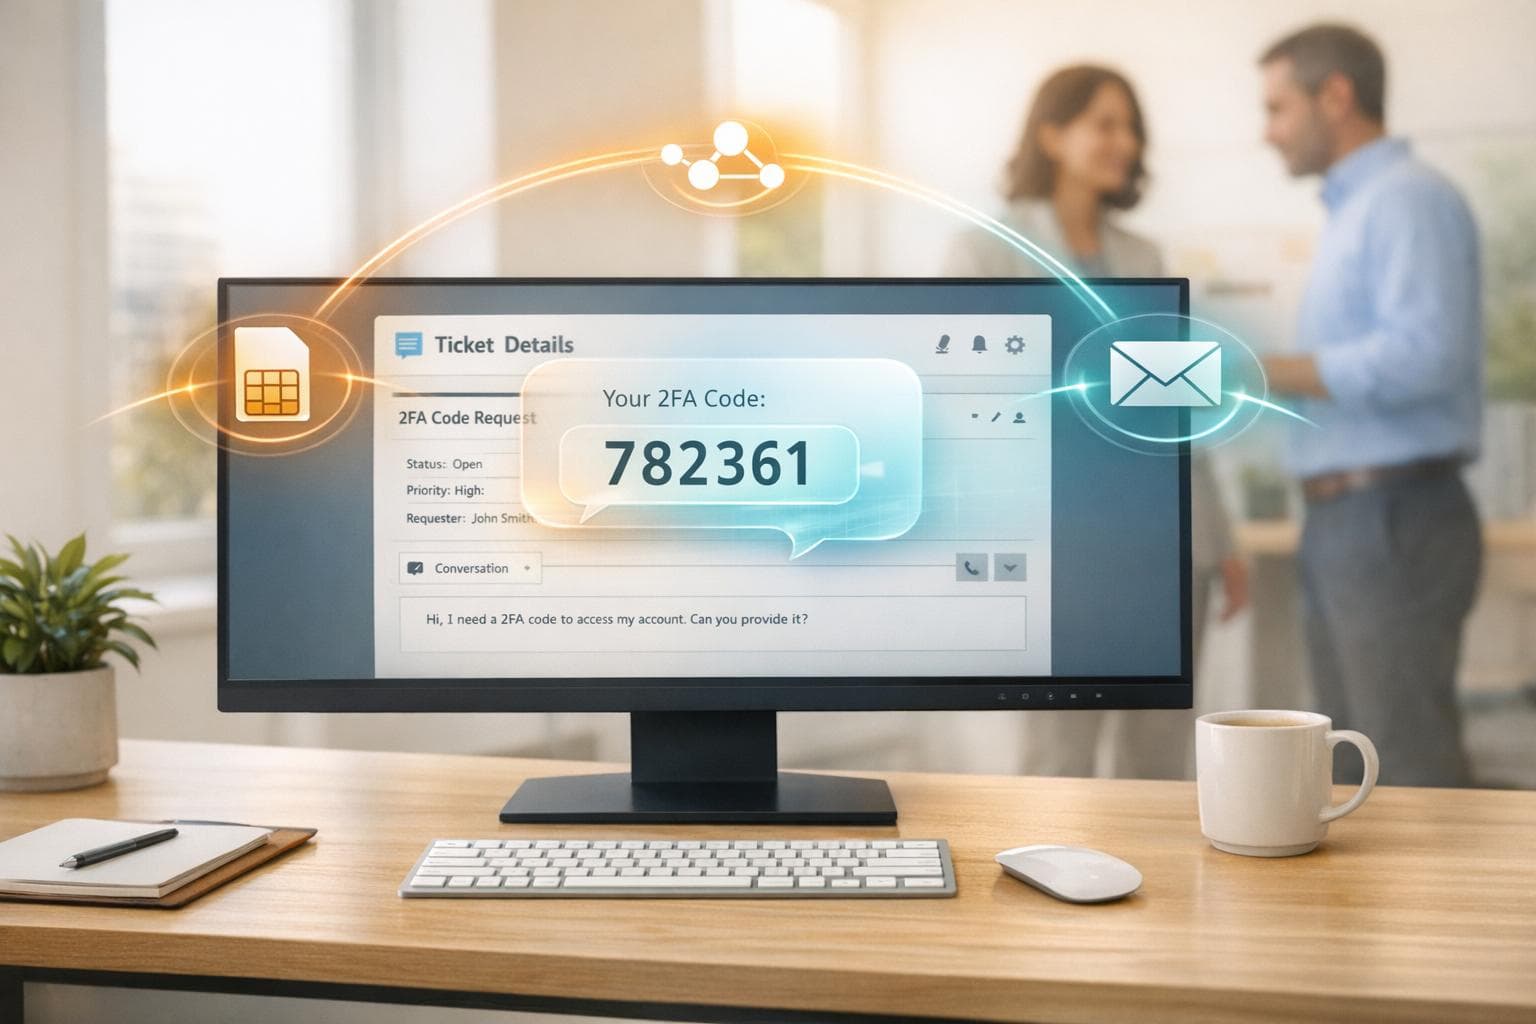
Account Management
Route 2FA SMS into your helpdesk using a real‑SIM number, webhooks or email to centralize access, create an audit trail, and prevent lockouts.
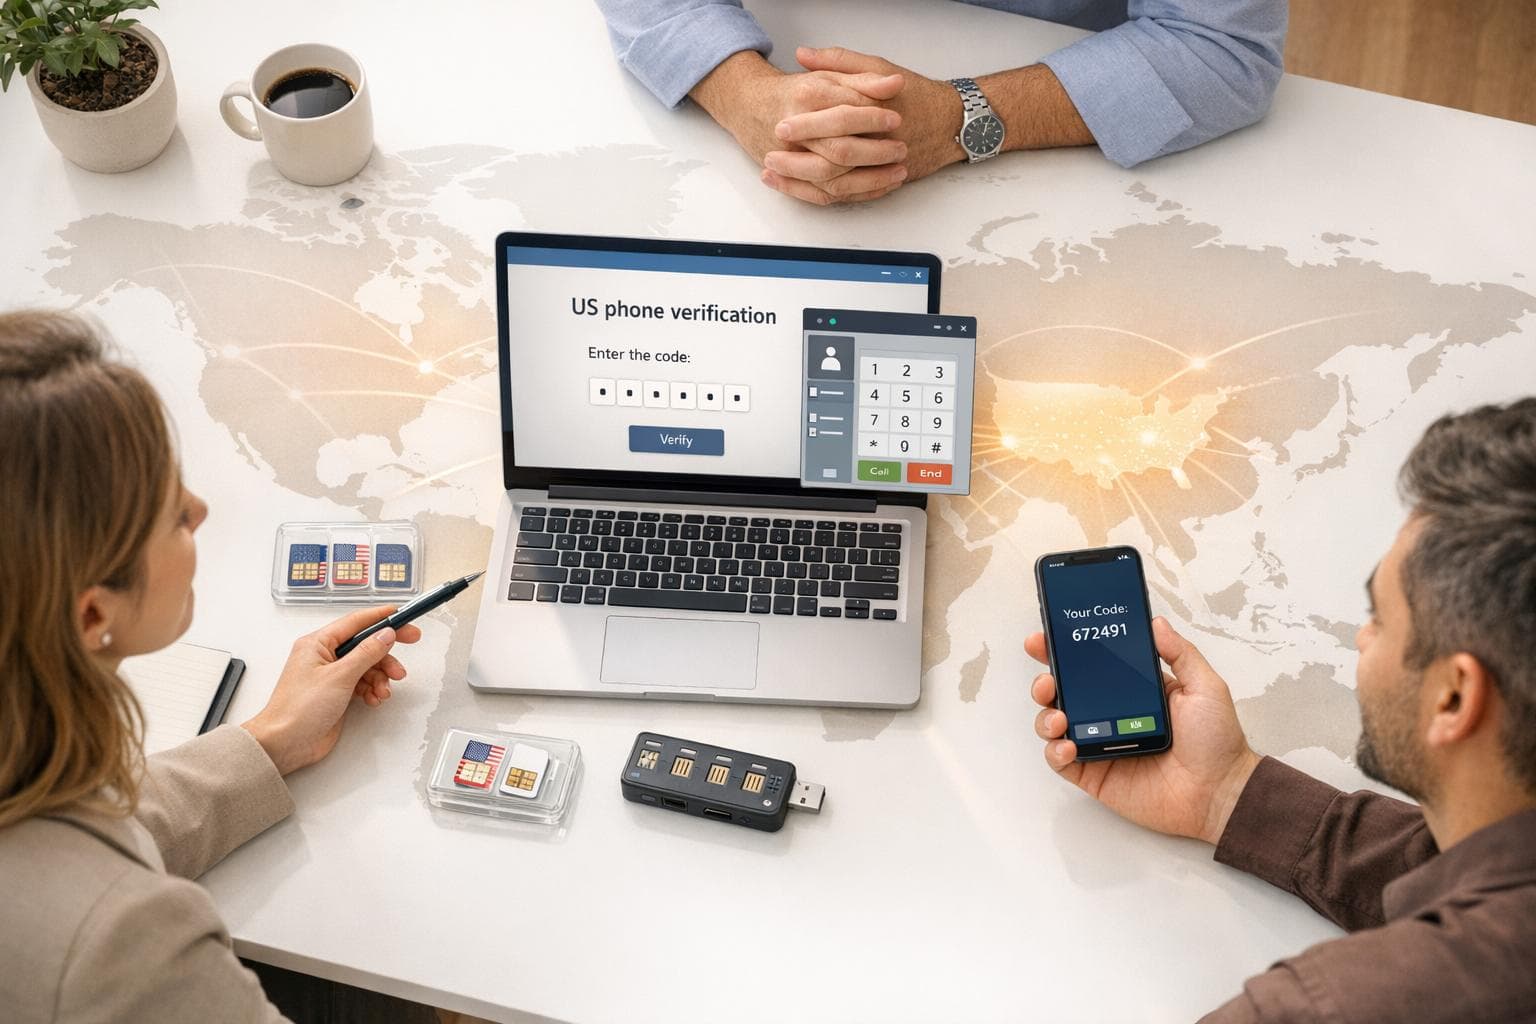
Account Management
Compare physical SIMs, real-SIM rentals, and VoIP to pass US-only phone verification—practical setup, costs, and best practices for non-US teams.
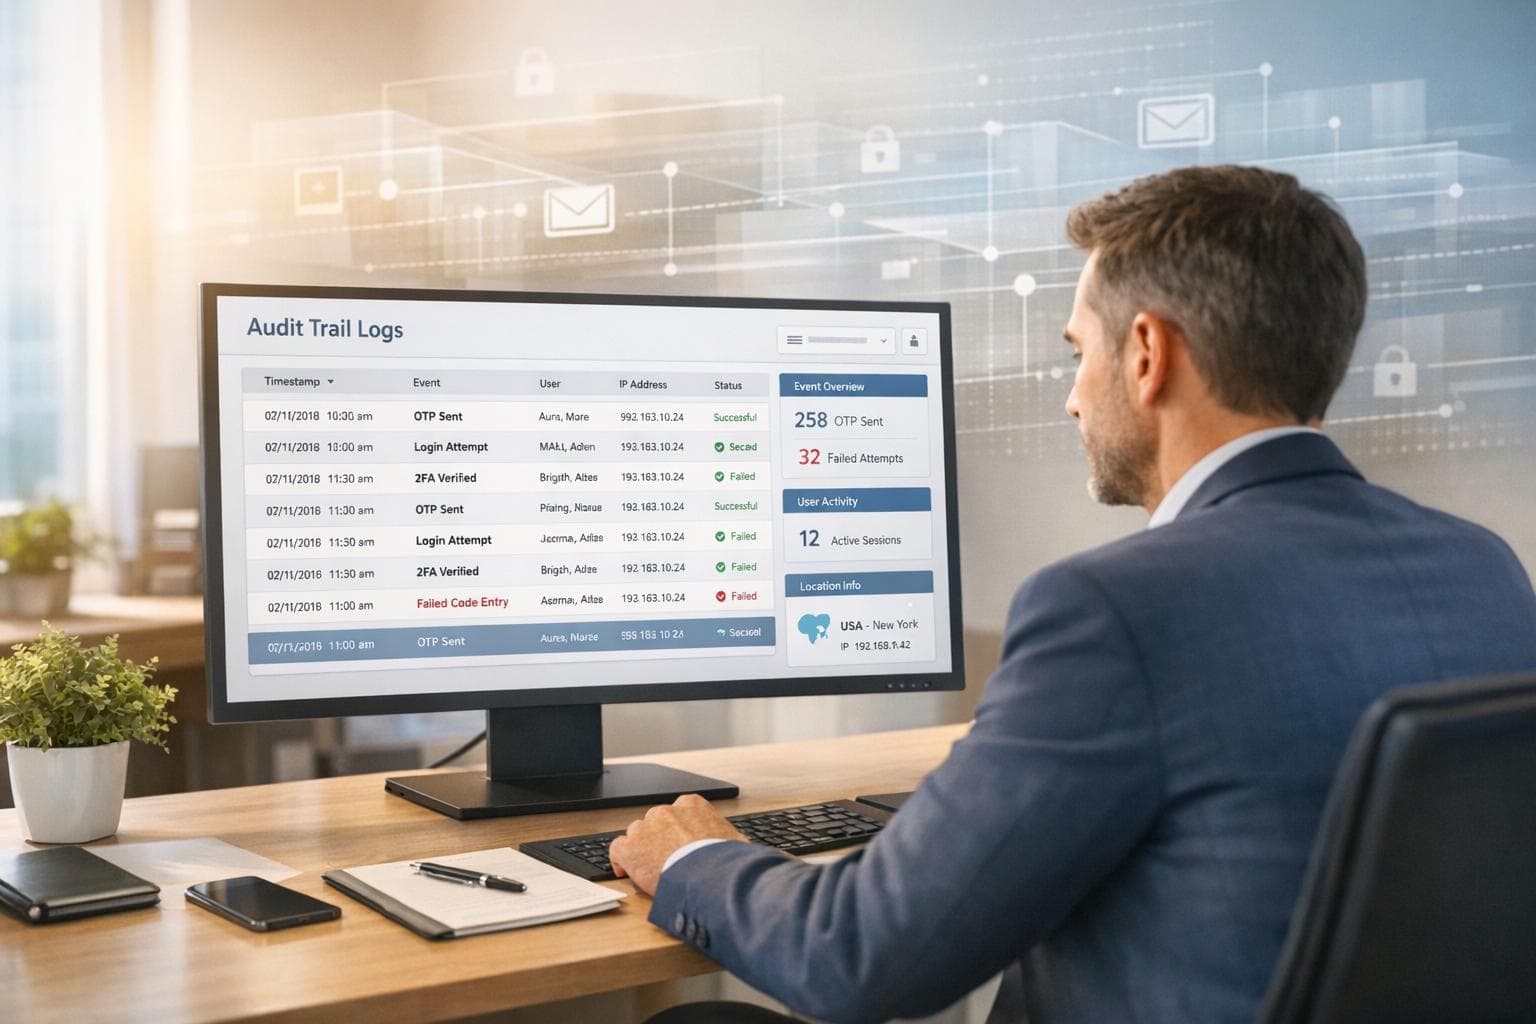
Account Management
Build tamper-proof OTP audit trails for 2FA: event logging, metadata capture, secure storage, retention policies, and real‑SIM SMS delivery.